Playbook: prove that the check happened
The situation
The auditor asks whether sanctions screening happened before the shipment to a customer outside the EU. It did — in someone's head.
Before you start
- Rules start in Monitor: they record what they would have done. Switch to Warn or Block per rule when the process can follow.
- History records cannot be changed or deleted; the chain shows if anything was.
Step 1 — Rules from the list
Open Command → Compliance → Our regulatory list → Rules.
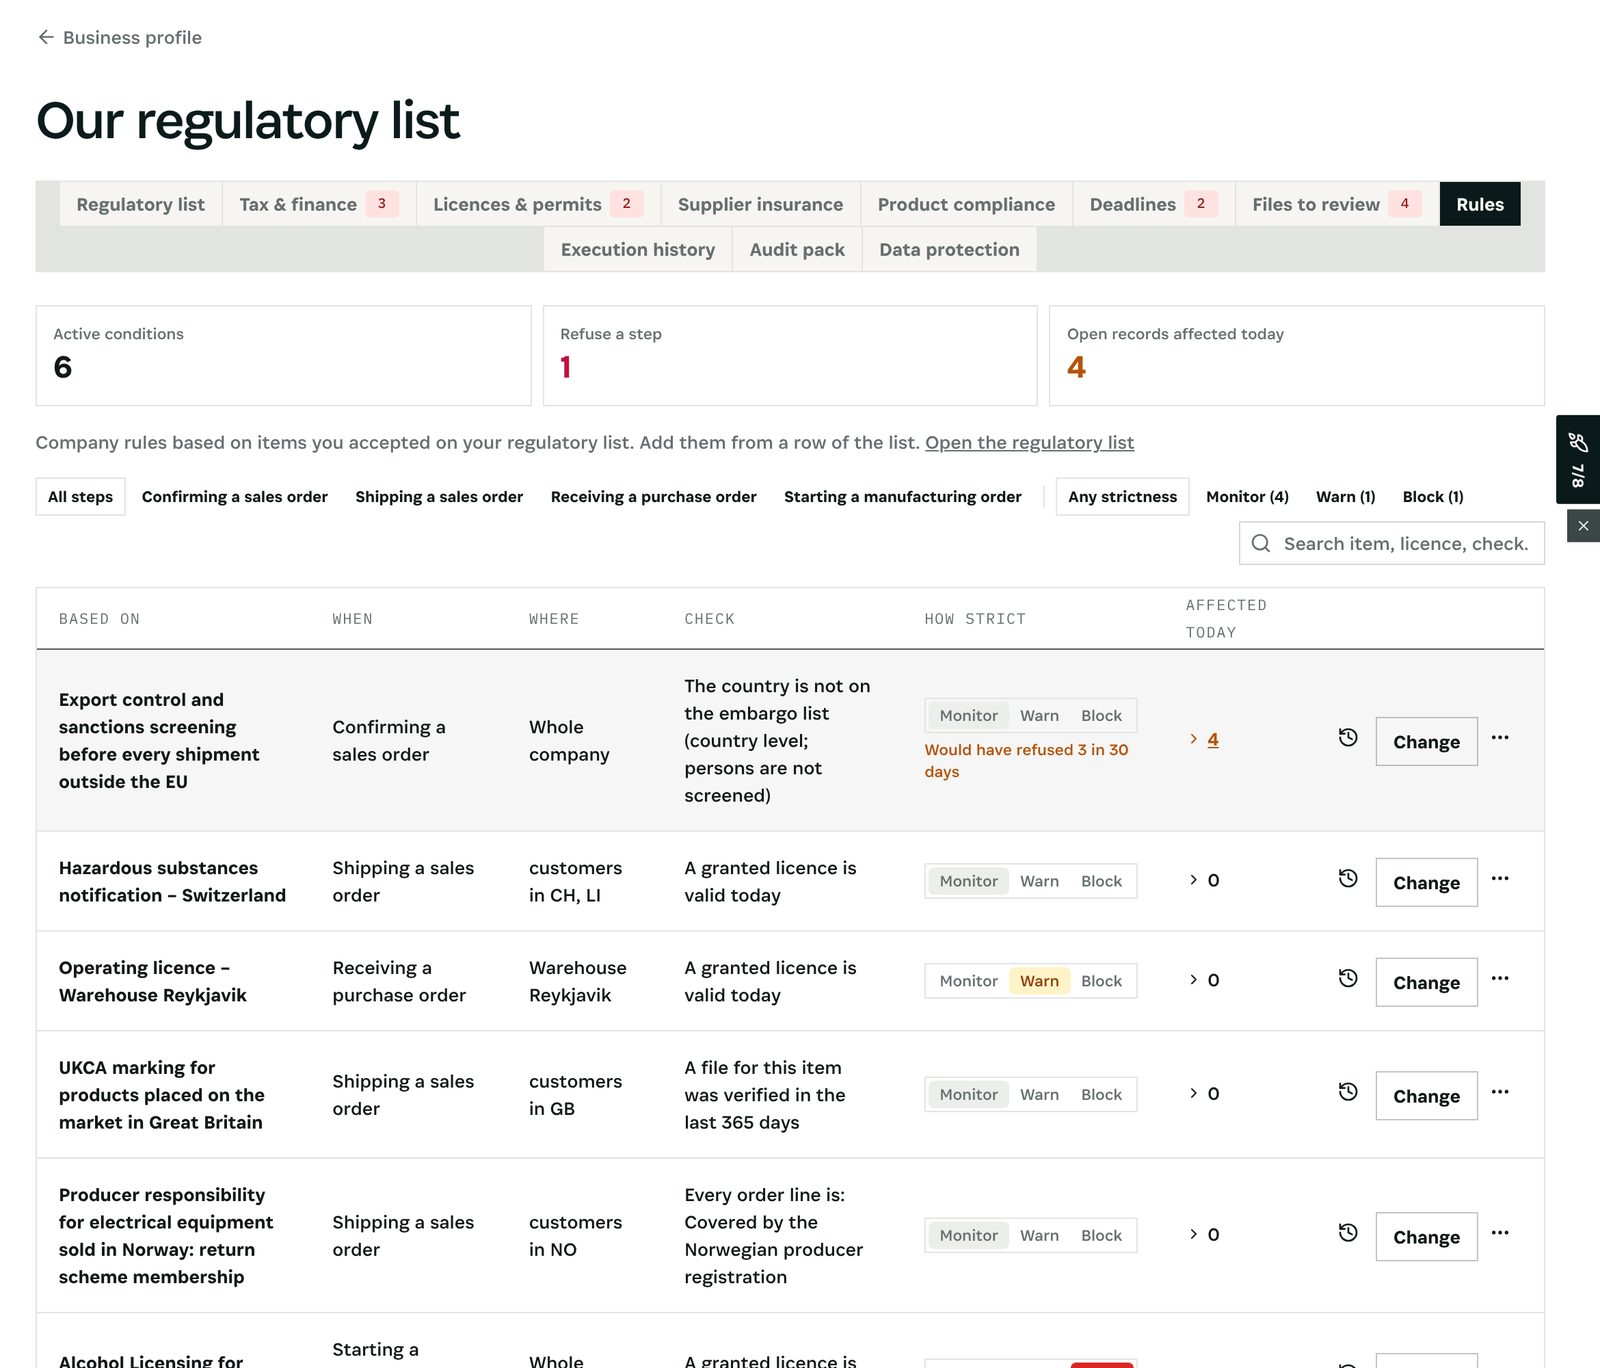
What you see: rules built from items on your list, each with its step, place, check and strictness. In the demo: export control and sanctions screening before every shipment outside the EU (monitor; *would have refused 3 in 30 days*), the Swiss hazardous-substances notification for customers in CH and LI, the Reykjavik operating licence when receiving (warn), UKCA for customers in GB, Norwegian producer responsibility.
Step 2 — The history
Choose Execution history.
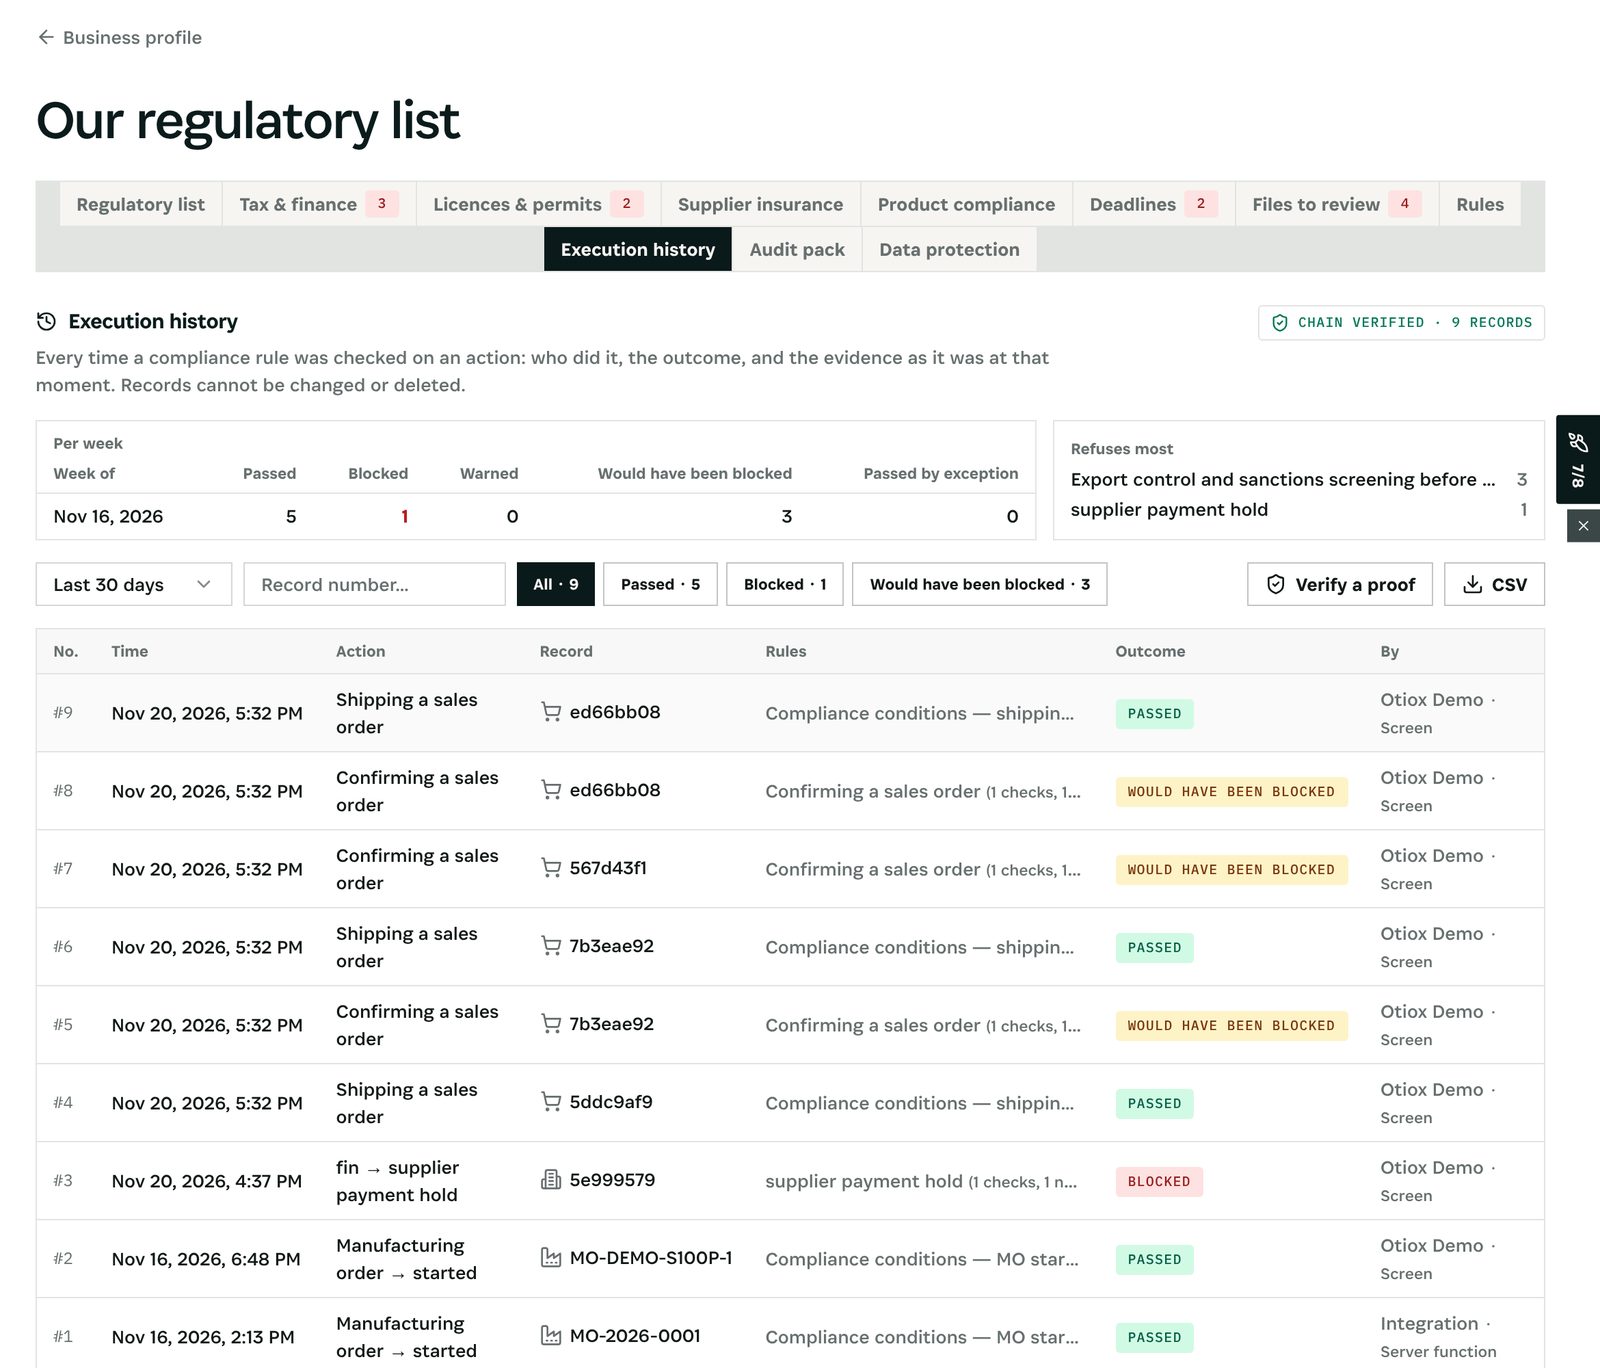
What you see: every time a rule was checked on an action — who did it, the outcome and the evidence at that moment. In the demo 9 records: 5 passed, 3 would have been blocked (the sanctions rule in monitor), 1 blocked (a supplier payment hold). Chain verified; Verify a proof checks a single record; CSV exports the list.
Step 3 — The audit pack
Choose Audit pack.
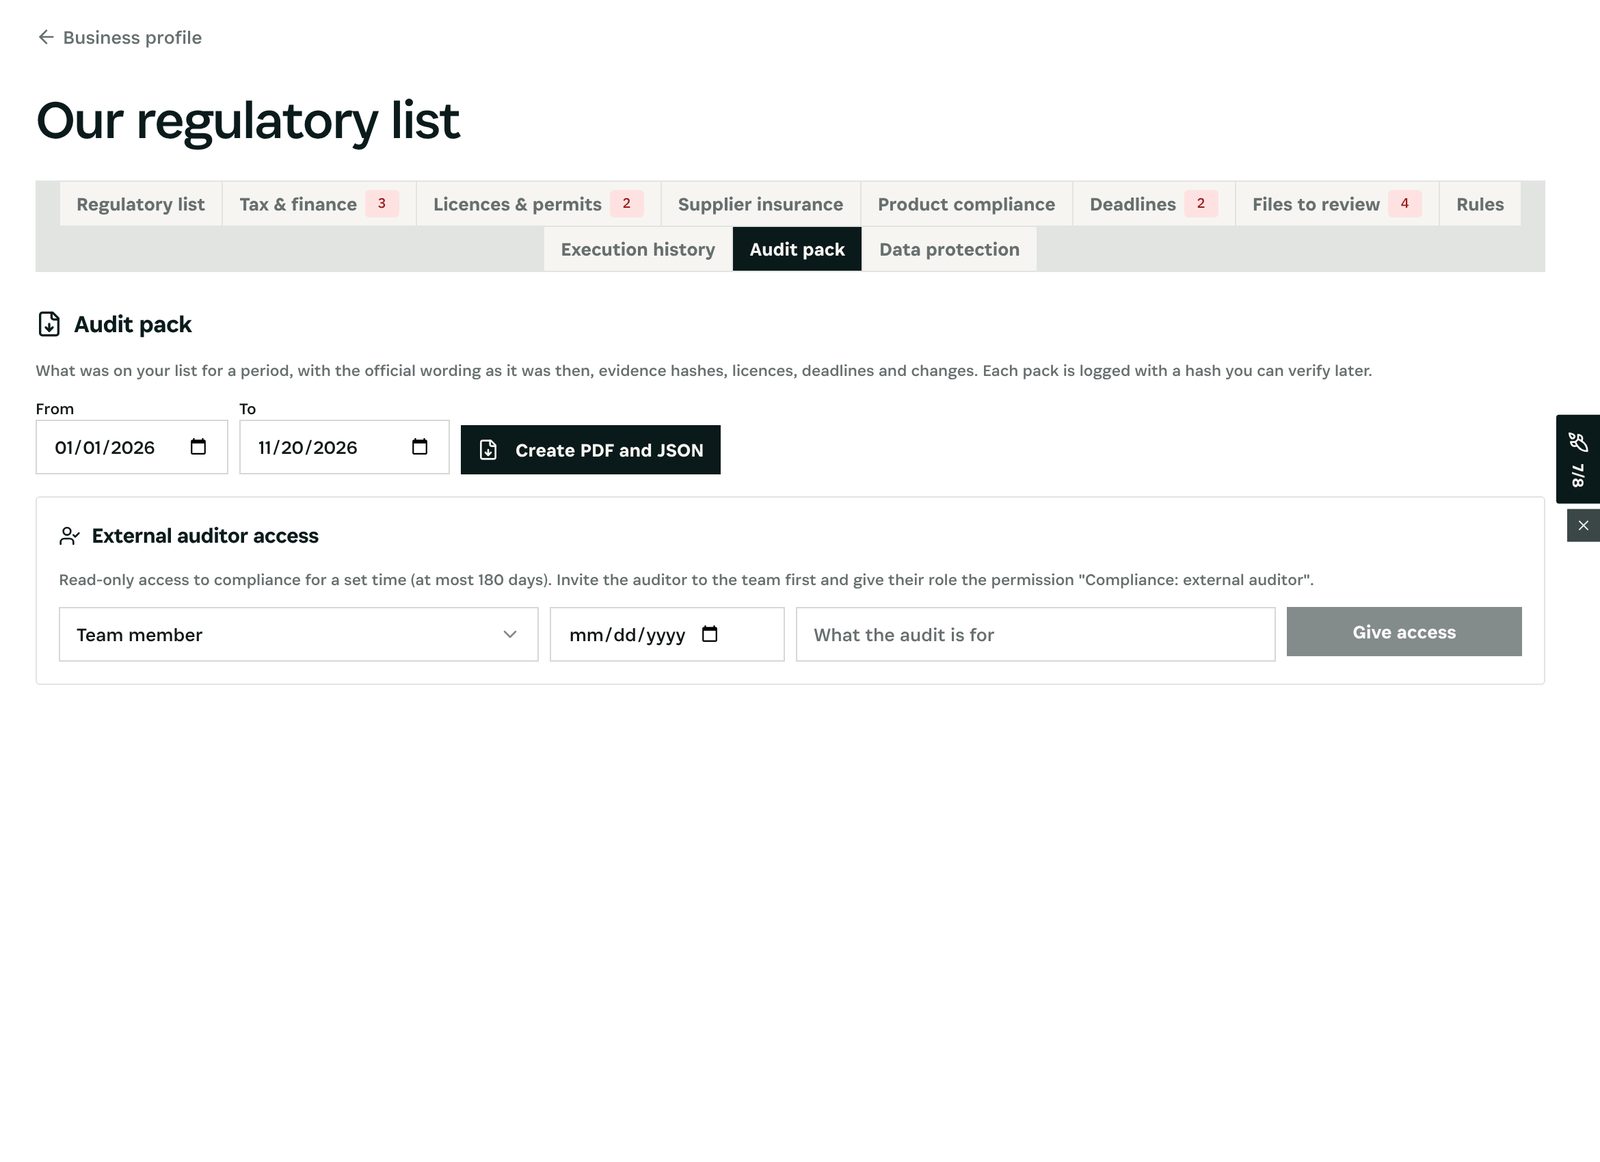
What you see: choose the period and Create PDF and JSON: what was on your list, with the official wording as it was then, evidence hashes, licences, deadlines and changes. Each pack is logged with a hash you can verify later. External auditor access gives read-only access to compliance for a set time (at most 180 days); what they open is logged. Data protection sets retention per kind of file and legal holds that stop deletion.
What you have at the end
- Rules that run on real steps, rolled out safely.
- A history the auditor can verify.
- The audit pack on demand.
Screenshots come from the Otiox demo workspace. Choose Switch to demo in the sidebar to follow along; changes there never touch live data.